Skip to content

Don't Accidentally Serve Dotfiles With Nginx

View on Twitter

💡 When serving your frontend app directly through Nginx, make sure to not accidentally expose any dotfiles.

👉🏼 Add a location directive to your server configuration to block access to all hidden files.
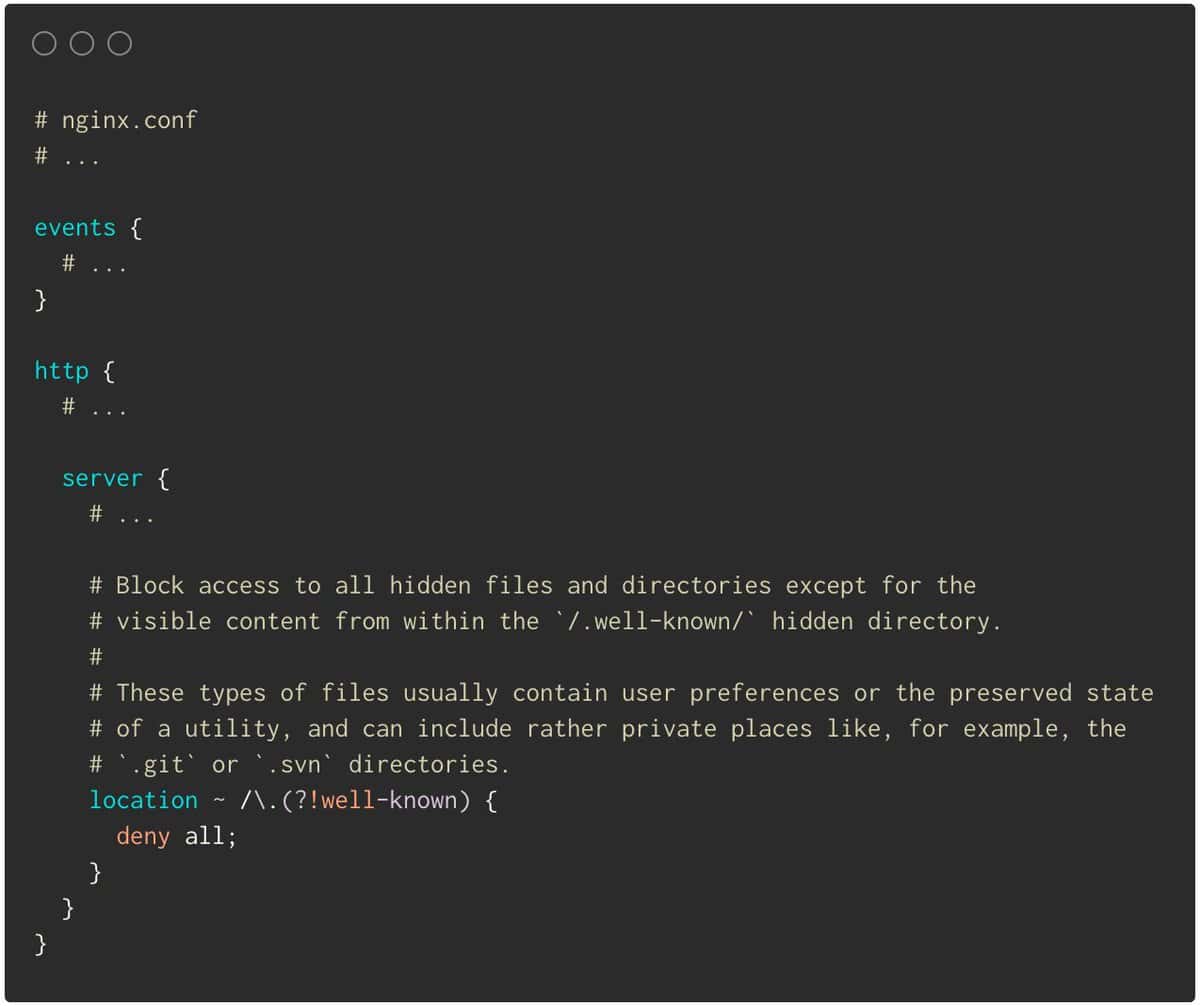
Add deny all inside a location block matching ~ /\.(?!well-known) paths to not serve dotfiles in your project.

Download the VPS Security Cheatsheet

Use this FREE security cheatsheet to not miss a step when securing your VPS.

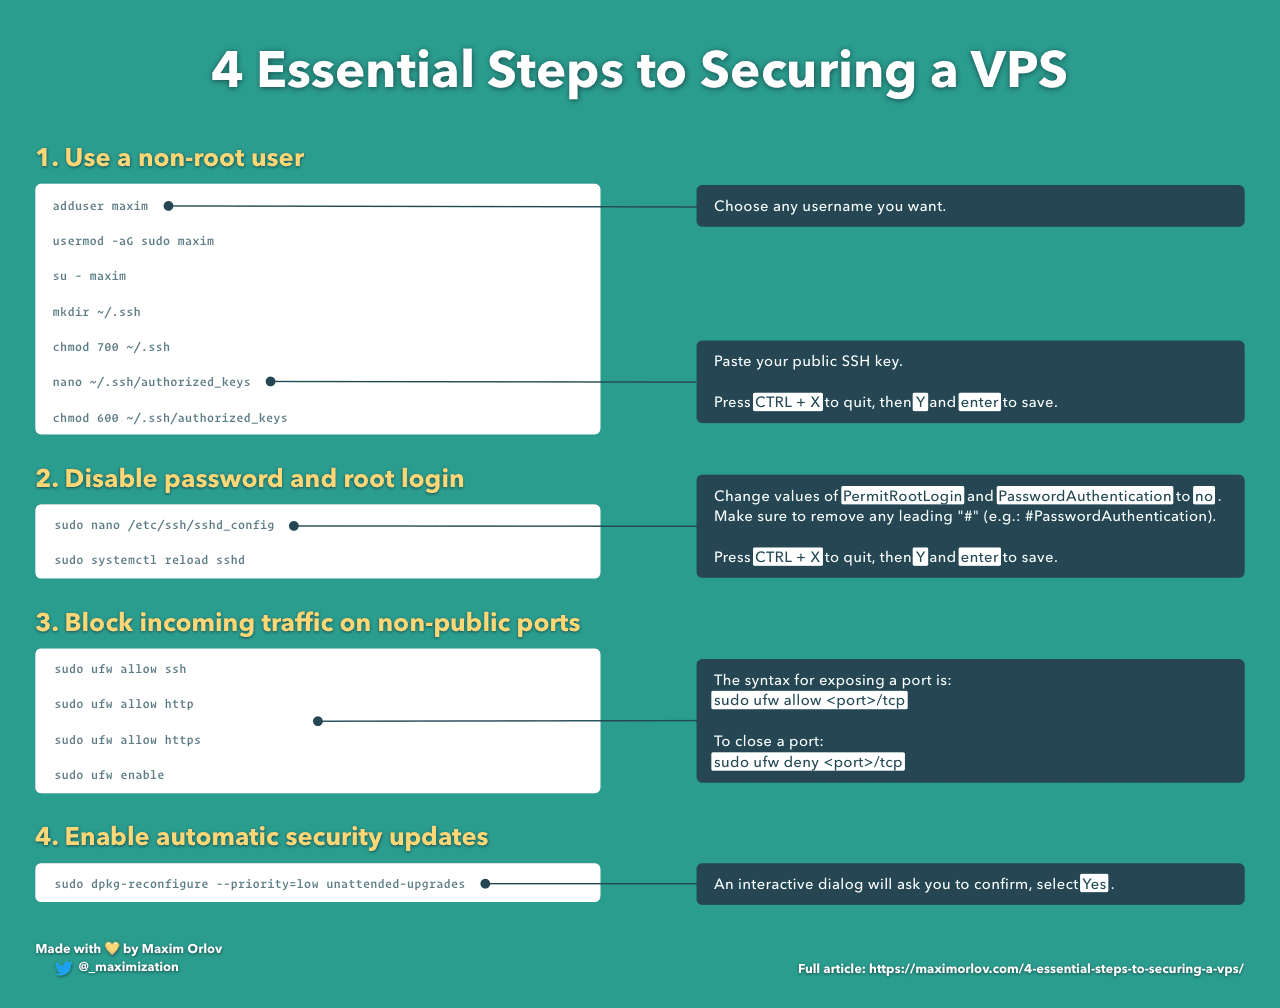
A preview of the VPS Security Cheatsheet.

You'll also get tips on building scalable Node.js applications about twice a month. I respect your email privacy. Unsubscribe any time.

You might also like
Strict vs Non-Strict Mode in ECMAScript Read tip
Find Nearest Tailwind Colour Read tip
Quickly Navigate to Folder in Shell Read tip